Your IT team protects devices long before they reach retirement, using encryption, access controls, device management, and internal erasure procedures. Those measures help protect sensitive information throughout the equipment’s working life.
An encrypted device can still hold sensitive data, though. Encryption controls who can read that information, and sanitization is the separate step that prepares the equipment for another owner. Retirement calls for its own security process to handle that step and document it.
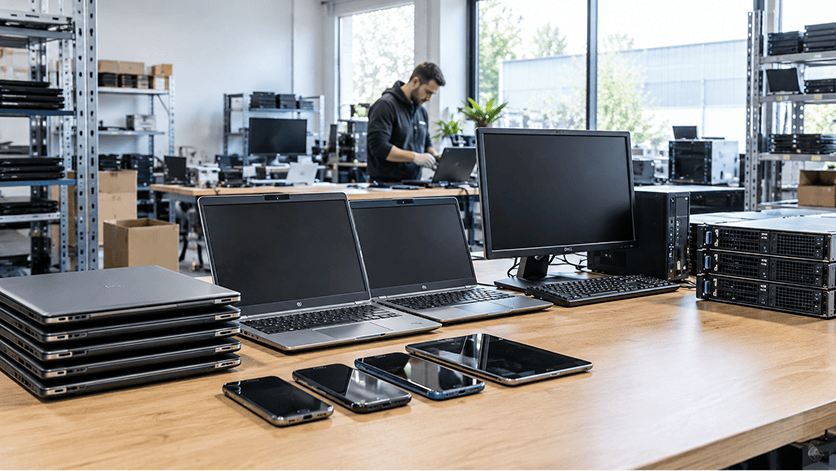
At OEM Source, we add specialist support and documented accountability to the measures your team already takes. Secure handling, appropriate sanitization, verification, and reporting connect each device in the agreed inventory to a documented outcome. Once your security requirements are met and reuse is authorized, eligible equipment can be refurbished and remarketed, and the remaining materials go to responsible recycling.
Encryption Is Valuable Protection, With Important Limits
Encryption makes stored information unreadable to anyone without the right cryptographic keys. When it’s implemented and managed well, it provides strong protection against unauthorized access.
That protection depends on the system around it, including how the keys are stored and how the device is configured. Attackers often go after a weakness in that system and leave the encryption algorithm itself alone. Depending on the device and whether it’s running, attacks may target keys held in memory, exposed hardware interfaces, or flaws in the boot process. Microsoft’s BitLocker guidance describes these attack paths and the controls that reduce them.
Encryption is strong protection, but it doesn’t eliminate every way someone might access the data.
Knowing that encryption was turned on also leaves several retirement questions open. Your team still needs to confirm that a suitable sanitization process ran and succeeded, and that every outgoing device was included.
Future Threats Make Long-Term Confidentiality a Planning Factor
Some information stays sensitive long after the equipment storing it has lost its business value, and a retired laptop may hold records that need protecting for many years.
Quantum computing raises questions about how long today’s encryption will remain secure. The expected threat to certain public-key systems differs from the threat to symmetric encryption such as AES, which commonly protects stored data. NIST expects AES-192 and AES-256 to stay secure against known quantum approaches for a very long time.
Even so, NIST SP 800-88 Rev. 2 lists long-lived sensitive information as a factor when evaluating cryptographic erase. Because the ciphertext stays on the media, future weaknesses or advances that allow key recovery could affect it. Organizations can plan for this without predicting when such an attack becomes practical, by choosing sanitization based on how long their information must stay confidential.
Choose Sanitization That Fits the Media and the Requirements
NIST describes sanitization as making access to target data infeasible for a specified level of effort, and its three methods meet different needs:
- Clear: Addresses user-accessible storage and protects against simple recovery techniques.
- Purge: Protects against advanced laboratory recovery while potentially preserving the media for reuse. Suitable device-supported techniques can reach storage areas that ordinary overwriting misses.
- Destroy: Makes recovery infeasible and leaves the media unable to store data.
Cryptographic erase is a recognized Purge technique when its requirements are met. It sanitizes the cryptographic keys and leaves the encrypted data behind, which makes it a separate step from having encryption turned on.
The right choice depends on the media, how its encryption is implemented, how sensitive the information is, and how long it must stay confidential. For your team, the key test is whether the selected process meets your requirements for that equipment. A trusted ITAD partner helps set those requirements and document the outcome.
A Second Layer of Protection for Your Existing Process
Your team may have already erased devices before arranging pickup, and that work is an important part of your security program. We complement it with a controlled disposition process which includes sanitizing all information storage media received, even when a client has performed its own erasure. We do not assume equipment is ready for reuse simply because it arrives labeled “wiped”.
This approach supports our R2v3 sanitization obligations and adds another layer of protection to your existing process. We reconcile received equipment against the agreed inventory, document sanitization results, and address discrepancies or failed attempts. Media that cannot be successfully sanitized for reuse follows the appropriate physical destruction process.
For your team, that means a documented outcome supported by our own processing – not just an assumption that an earlier erasure was completed successfully.
A refresh or cleanout should establish:
- Agreed inventory and scope: The equipment being transferred, its available identifiers, and the required disposition outcomes.
- Documented custody: A record of equipment movement and handoffs through collection and processing.
- Receipt and reconciliation: A comparison of received equipment against the agreed inventory, with any differences investigated.
- Appropriate sanitization: A process suited to the media and your security requirements.
- Reviewed results: Verification that sanitization completed, followed by validation that the outcome is acceptable.
- Exception handling: A path for missing equipment, failed sanitization attempts, and devices that need further action.
Verification checks the sanitization outcome; validation determines whether that outcome is sufficient. An unacceptable result goes back for further sanitization or escalates to a stronger method. This is the second layer of protection in practice, with an accountable path for every device, including equipment that can’t move through the process normally.
Reporting Makes the Process Reviewable
Detailed reporting gives your team evidence it can review, keep, and use to answer internal questions. Useful records connect each device or media identifier to the sanitization method, tool, and result, along with relevant verification details. Discrepancies and exceptions get documented outcomes as well.
SERI’s R2v3 guidance emphasizes device-specific sanitization records and controls for evaluating how well the process works. Those records help show what happened to each identified device.
Our R2v3 and NAID AAA certifications support your due diligence within their applicable scopes. R2v3 requirements cover defined facility activities, and NAID AAA includes scheduled and unannounced audits of certified services. Their practical value shows up in the handling, processing, and reporting we provide for your project.
Security Creates the Conditions for Reuse
A secure disposition process also preserves the value of equipment that can keep serving another user. Once sanitization is accepted and reuse is authorized, eligible devices move on to testing, refurbishment, and remarketing. Recovery value depends on factors such as age, specifications, condition, and market demand.
Media that can’t meet the agreed sanitization requirements through a reuse-preserving process goes through appropriate, documented physical destruction. Where practical, replacing that media lets the rest of the device be reused, a pathway SERI recognizes for otherwise functional equipment. Equipment and materials unsuitable for reuse then move through responsible recycling.
Plan a Secure Refresh or Cleanout with OEM Source
Your team’s existing safeguards give retirement a strong foundation, and we add specialist handling, sanitization, and documentation to carry that protection through each device’s next transition. Whether you’re planning a refresh or emptying a storage room of old equipment, the work starts with an agreed inventory, defined security requirements, and set reporting expectations.
Contact OEM Source to plan a secure refresh or cleanout that supports data protection, value recovery, and responsible recycling.